Risk often becomes interesting at the worst possible time.
A customer complains. A regulator asks a question. A vendor fails. A key employee leaves. A system goes down. Leadership gathers in a room and asks when someone first knew there was a problem.
Usually, someone knew something.
They saw the recurring exception. They noticed the unsupported system. They knew the contract commitment wasn’t being met. They watched the workaround become normal. What the organization lacked wasn’t awareness. It lacked a reliable path from concern to decision.
We need updates before the damage is done.
That’s the practical purpose of governance. It isn’t a committee, a binder, or a yearly exercise performed for an auditor. Governance defines who can decide, what evidence they need, when an issue must be escalated, and how the organization knows the decision was carried out.
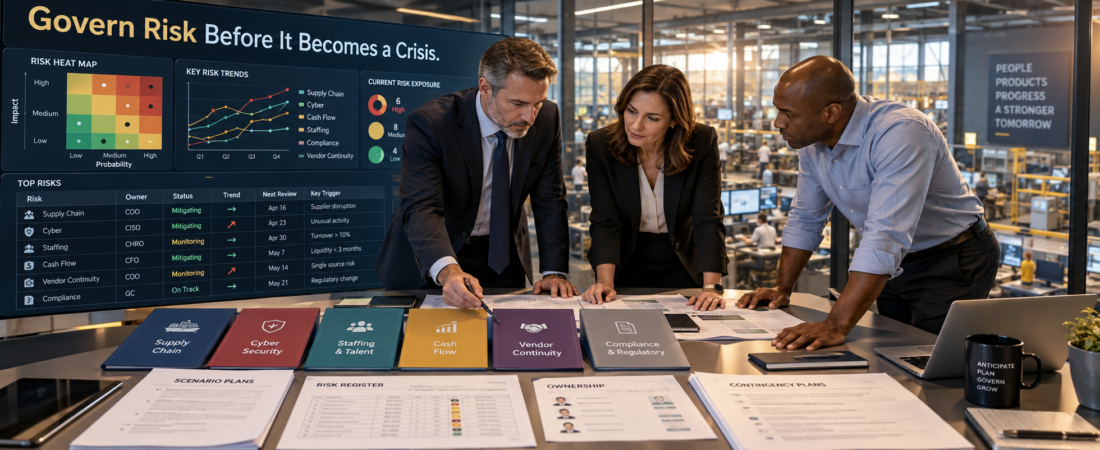
Risk management fails when it’s separated from the work. Employees complete a questionnaire once a year while the underlying operation changes every week. A risk register records a concern, but no one owns the treatment. Leaders receive reports that classify everything as red, yellow, or green without explaining what decision is required.
Color isn’t control.
Begin with a consequential operating area. Customer data is one example. Ask where it enters, who can access it, which vendors touch it, how it moves, how long it remains, and what happens when something goes wrong. The answers will cross departments because risk doesn’t respect the organization chart.
Then assign a real owner. Ownership means the authority and obligation to act, not simply a name placed in a spreadsheet. The owner should know the expected condition, current evidence, accepted exceptions, next review, and point at which leadership must become involved.
Leaders also need to distinguish risk acceptance from neglect. An organization can knowingly accept a risk when the reasoning, authority, duration, and conditions are clear. Silence is not acceptance. An old issue with no decision is not acceptance. A leader saying “we’ve always done it this way” is not acceptance.
Nothing is ever ‘Always’!
Conditions change. Vendors change. Employees change. Laws, systems, customers, and threat patterns change. A control that worked two years ago may now protect a process that no longer exists.
Useful governance creates a cadence for examining evidence and making decisions while options are still available. It connects the boardroom to the operating floor without turning every exception into a crisis meeting.
Review one current risk. Can you name the owner, the evidence, the decision authority, the treatment, and the next review date? If not, you may have recorded the risk without governing it.
Wentworth Consulting Group, LLC helps organizations turn risk and governance into visible operating disciplines—so leaders can make informed decisions before the cost becomes a crisis.